About USUA LLC

About USUA LLC

USUA LLC is a Texas-based cloud security engineering company specializing in Cloud Identity and Access Risk Management, privileged access, and cloud access security.

We help organizations reduce access risk across AWS, Microsoft Azure, and Google Cloud Platform (GCP) — without introducing controls that make cloud environments unnecessarily difficult for engineering teams to operate.

AWS Microsoft Azure Google Cloud Platform (GCP)
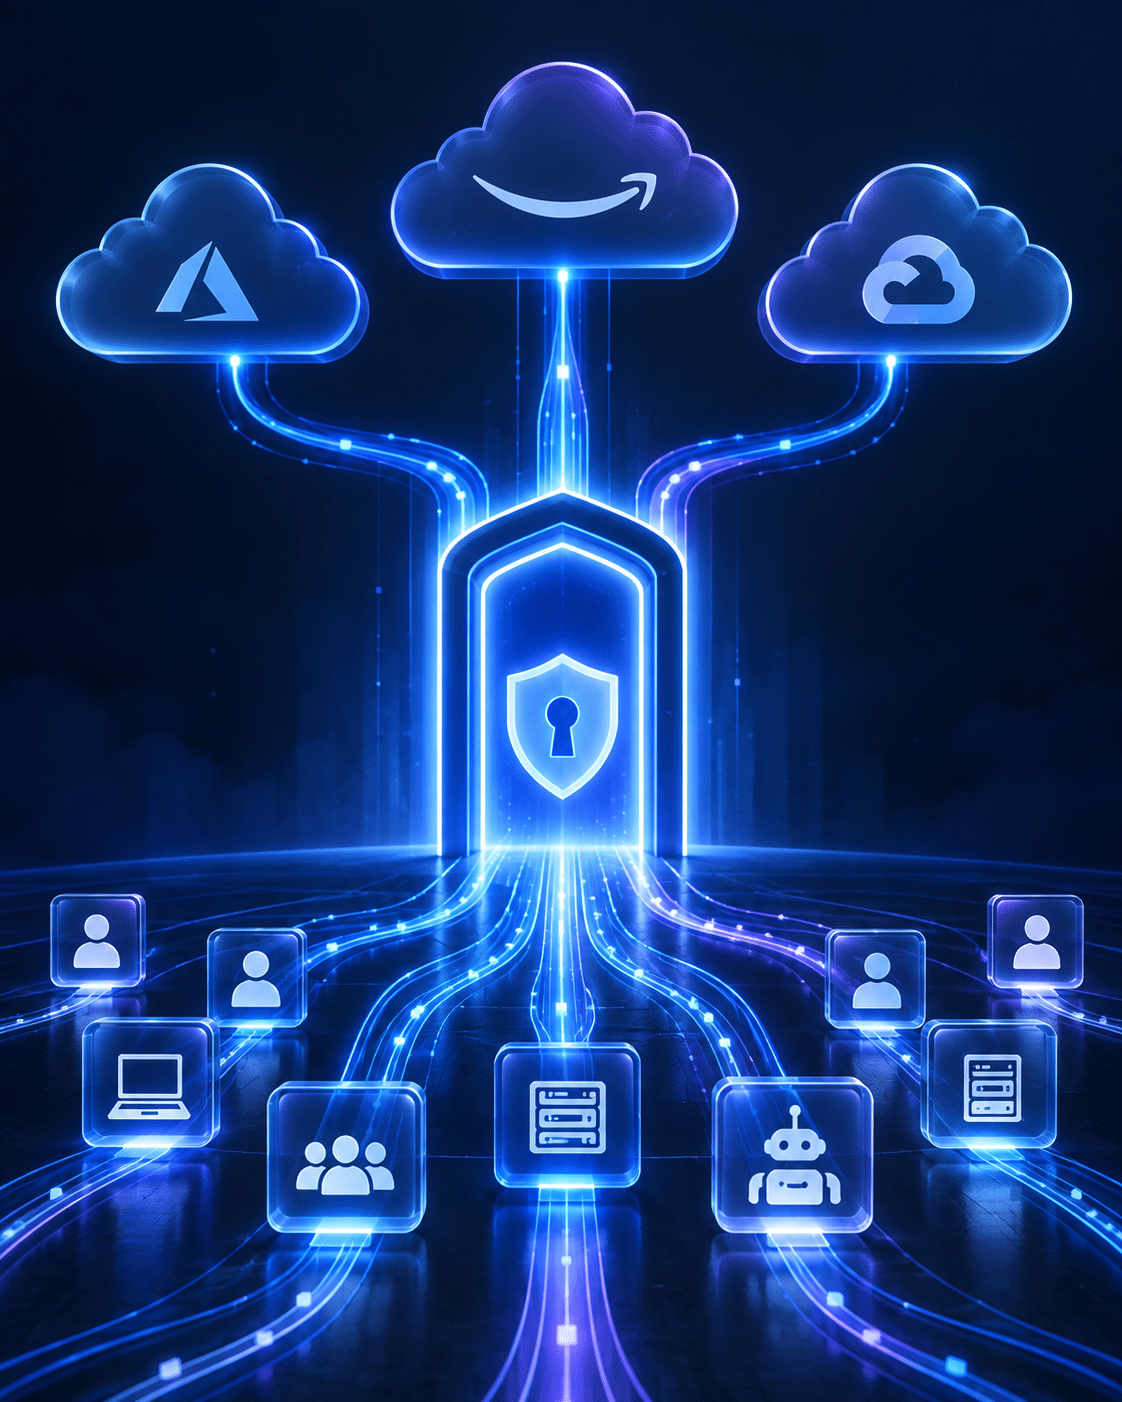
Human and machine identities passing through a single secure access gateway into AWS, Microsoft Azure, and Google Cloud
Our Mission

Give every human and machine identity the access it needs—when it needs it—and no more.

Our work goes beyond reviewing IAM policies.

We work directly with cloud and identity environments to identify excessive permissions, standing administrative access, dormant identities, external trust relationships, risky service accounts, API keys, and other non-human (NHI) and machine identity risks.

We then help clients remediate these issues

and establish controls that remain manageable over time.

Our goal is straightforward:

Give every human and machine identity the access it needs—when it needs it—and no more.

CloudOps, DevOps, and security teams working together on a shared cloud access layer
Who We Work With

USUA LLC primarily works with small and mid-sized organizations that use public cloud infrastructure but do not have dedicated Cloud IAM specialists on staff.

We also support organizations preparing for or maintaining security and compliance programs where access governance, least privilege, privileged access, Multifactor Authentication (MFA), and identity controls are important requirements.

Our team works alongside CloudOps, DevOps, security, infrastructure, and governance teams to take ownership of complex access problems that often fall between traditional IT, cybersecurity, and cloud engineering functions.

Our Areas of Expertise

Our Areas of Expertise

We assess, design, and tune identity and access controls across AWS, Azure, and GCP. This includes permissions, roles, policies, federation, external access, service accounts, API keys, and NHIs.

Our focus is on reducing excessive and unnecessary access while maintaining the access engineers need to operate cloud infrastructure effectively.
Cloud IAM & Access Security

We assess, design, and tune identity and access controls across AWS, Azure, and GCP. This includes permissions, roles, policies, federation, external access, service accounts, API keys, and NHIs.

Our focus is on reducing excessive and unnecessary access while maintaining the access engineers need to operate cloud infrastructure effectively.

Privileged Access & Zero Trust

We design and implement privileged-access architectures that reduce permanent administrative access.

This includes:

  • Privileged Access Management (PAM)
  • Just-in-Time (JIT) access
  • Temporary and time-limited privileged access
  • Zero Trust Network Access (ZTNA)
  • Privileged role management
  • Administrative access hardening

The objective is to replace unnecessary standing privileges with controlled, auditable access whenever practical.

Authentication & Federation

USUA LLC helps organizations strengthen how users authenticate and access applications and cloud environments.

Our work includes:

  • Tuning Okta and Microsoft Entra ID
  • Deploying phishing-resistant MFA solutions
  • Implementing passwordless authentication
  • Setting SSO federation between identity providers and cloud platforms
  • Configuring SAML
  • Building OIDC integrations between cloud and service providers

We place particular emphasis on modern authentication methods designed to reduce phishing and credential-based attacks.

Identity Governance & Machine Identities

Modern cloud environments contain many non-human identities: applications, workloads, automation pipelines, API keys, service accounts, roles, and other NHIs that can accumulate significant privileges over time.

USUA LLC helps organizations discover and govern these identities through:

  • Dormant identity identification and cleanup
  • Overprivileged identity remediation
  • Service-account governance
  • API-key lifecycle management
  • External and third-party access reviews
  • Access recertification
  • Offboarding and identity lifecycle controls
  • Cloud access monitoring and governance
How We Work

Our engagements typically begin with an assessment of the client's cloud and identity environment.

We identify access risks, determine where privileges can be reduced, and produce a prioritized remediation plan based on business impact and security exposure.

From there, USUA LLC can work directly with the client's technical teams to implement the remediation, redesign access where necessary, and establish ongoing governance.

A typical engagement follows four stages:

01

Assess

02

Prioritize

03

Remediate

04

Govern

This allows organizations to move beyond identifying IAM problems and actually resolve them.

Engineering-Focused Cloud Security

Cloud IAM projects often fail when security controls are designed without considering how engineers actually work.

USUA LLC approaches access security as an engineering problem as much as a security problem.

Controls must reduce risk, but they also need to support deployment pipelines, automation, operational access, incident response, and day-to-day cloud operations.

deployment pipelines
automation
operational access
incident response
day-to-day cloud operations
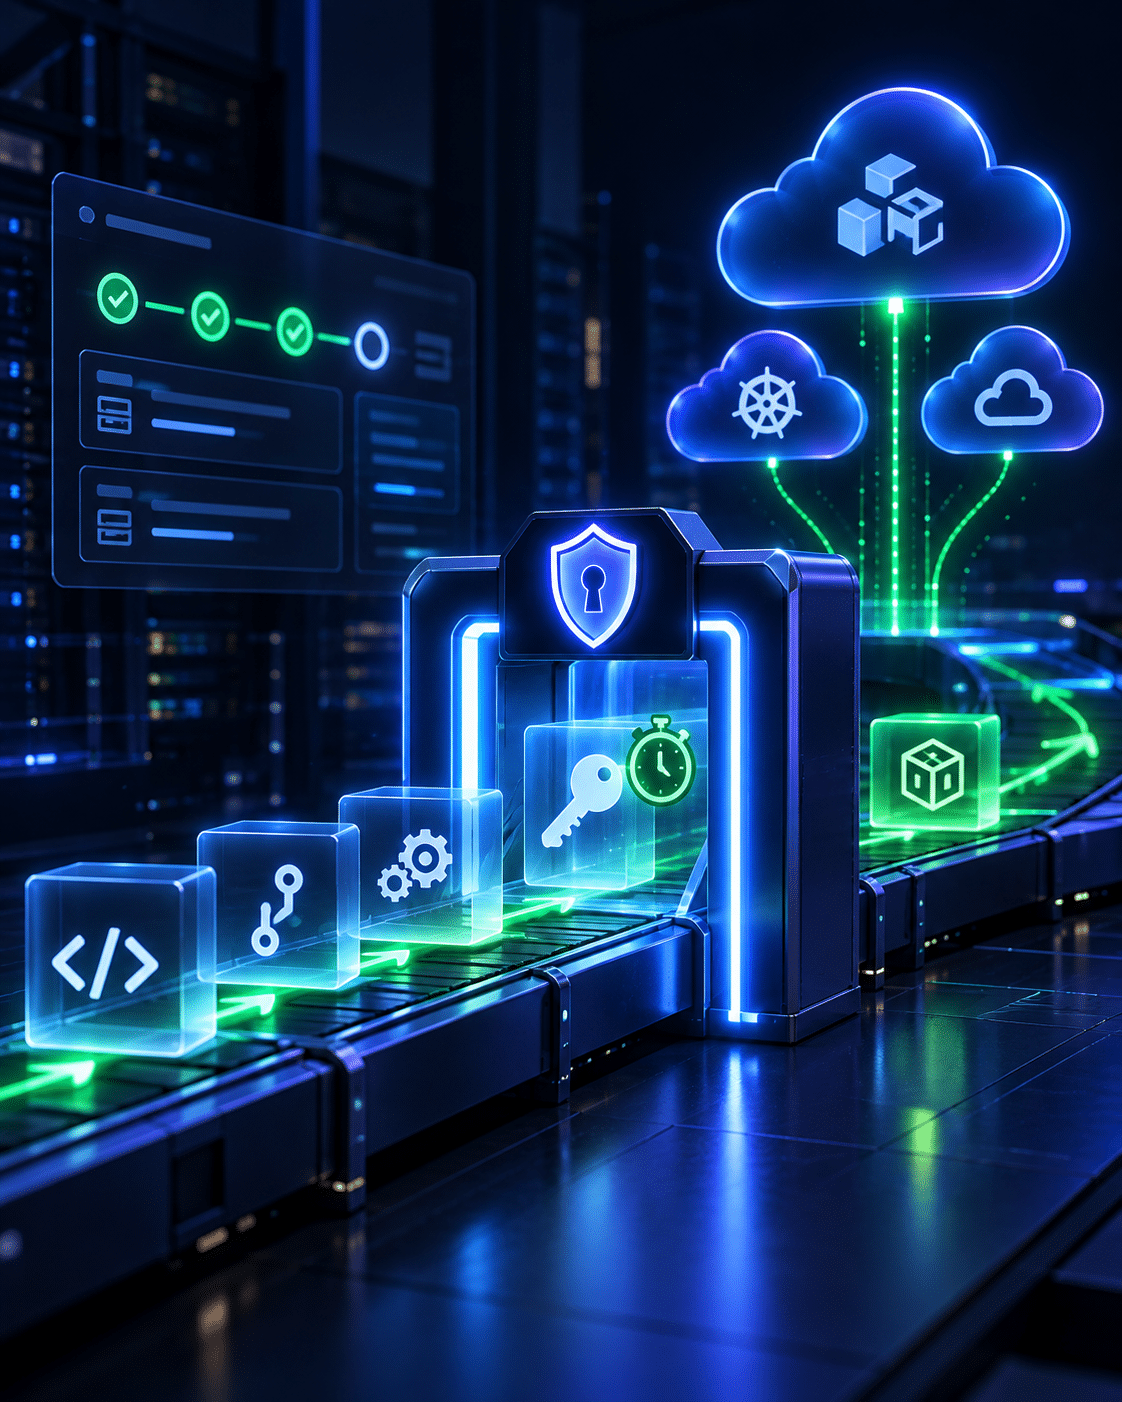
A CI/CD deployment pipeline passing through a temporary just-in-time access checkpoint before continuing to production
Need Help Strengthening Cloud Access?

If your organization needs deeper visibility into cloud access, stronger access controls, or hands-on help reducing excessive privilege, USUA LLC can help.

Start with a Cloud IAM assessment and identify the highest-priority access risks in your environment.

Schedule a meeting